This page documents exactly what happens between a branded search and a case landing in your workspace. Every stage, what gets captured, and where the method's limits are, so your legal or compliance team can evaluate it properly rather than take our word for it.
Before anything runs, we agree your branded keywords and their common variations, which countries and cities to check, which devices to observe, and how often. What isn't listed isn't scanned. Scope is fixed up front, not discovered as you go.
Search results are checked from the regions and devices your customers actually use, on the schedule you chose: a single one-time pass or continuous scheduled monitoring. Every check reads the same public page a real searcher would see.
Anything that looks unauthorized gets its redirect chain followed hop by hop, its tracking parameters extracted, and its partner or advertiser identified. It's checked against your roster, then packaged with timestamped screenshots into a case your team can open and act on.
Every case — hijacker or brand bidder — passes through the same seven stages before it reaches your workspace. Drag the scene, or pick a stage, to see where each one sits in the flow. This is the detail behind the three-step summary above, and behind every capability on the features page.
You and BrandPatrol agree the branded keywords to monitor, including common misspellings and variations, which countries and cities to check from, which devices to observe (desktop and mobile) and how often scans run. Anything not on that list is explicitly out of scope: it isn't scanned, and it isn't billed.
Before a single scan runs, we import your list of authorized partners. The affiliates, agencies, or resellers you've actually approved to bid on your brand — along with what each one is permitted to do. Every later detection is checked against this list first, so an approved partner never turns into a case you have to dismiss.
For each agreed keyword, from each agreed location and device, we check what's actually showing in the public search results — the same results page a real searcher would see, reached with no login and no special access.
When an ad on a branded term is found, we take a timestamped screenshot of the search-results page showing it, then follow the ad through to wherever it lands and screenshot that page too, along with the display URL exactly as it was shown in the ad.
The click isn't just followed to the final page. Every redirect hop in between is recorded in order, and the tracking parameters attached to each hop are extracted, because that's usually where the identifying information lives.
The tracking parameters are used to resolve which affiliate ID and which network the traffic is running through. Where the advertiser isn't one of your affiliates, we cross-reference the public ad-transparency record search engines already require, to identify who placed the ad.
The result goes through the roster check one more time. If it matches an authorized partner doing something they're approved to do, no case is filed. Otherwise a case is opened with a status your team can act on: new, in progress, solved, or muted.
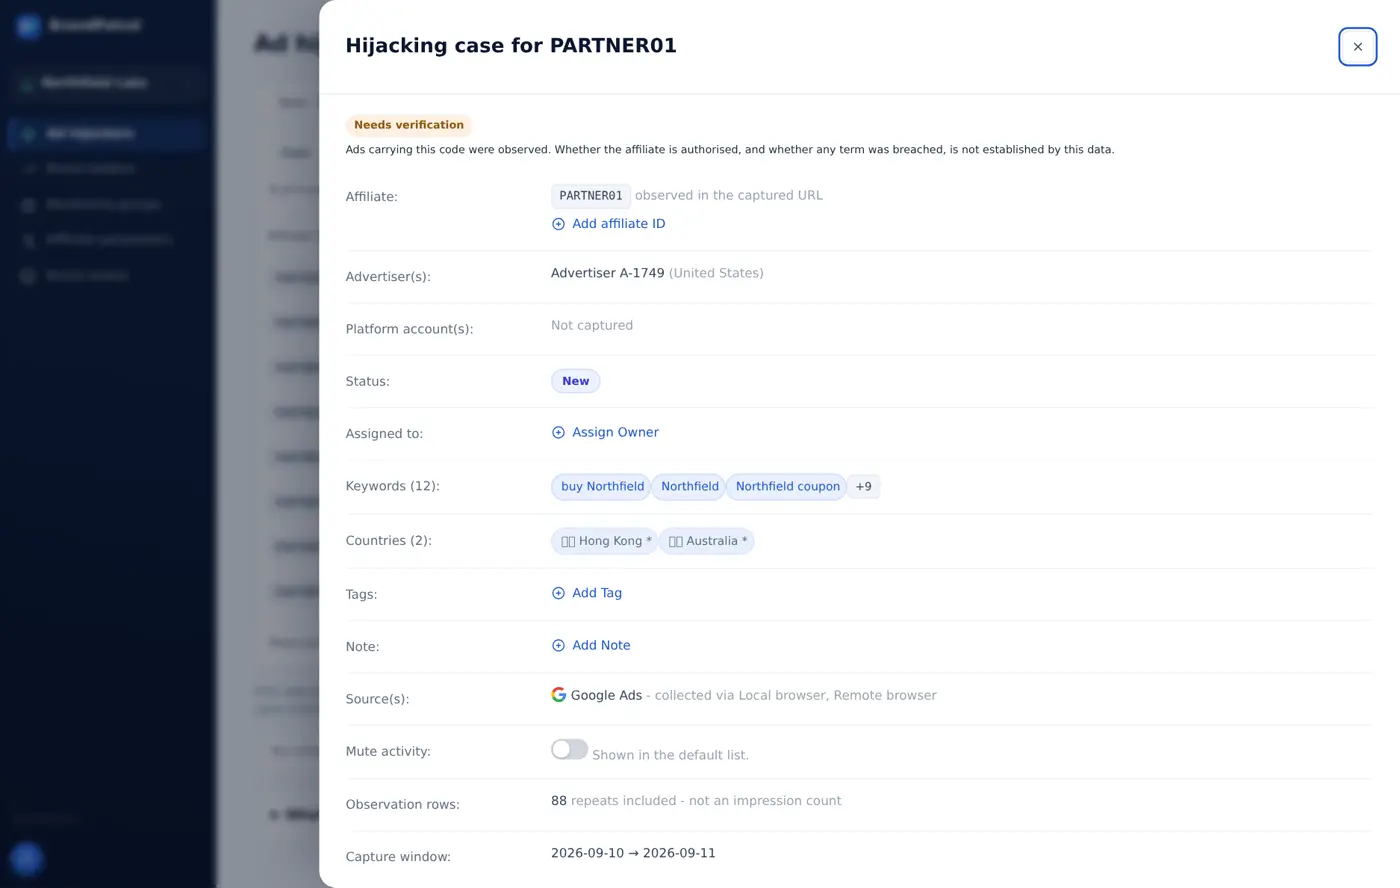
The result screenshot above is the end of the line. This is how a scan gets there, from search variants to sorted ads.
The scan starts from the branded keywords you scoped, including common misspellings and variations of the name, checked from the agreed countries and devices.
Each sweep reads the public paid results the way a shopper would see them, with no login. Every ad that shows up on a branded search appears as a blip.
An ad from your own official advertiser is cleared. An ad whose redirect chain carries a partner ID is marked as an affiliate. An ad with no partner ID at all is marked as a hijacker.
The totals build up as the sweep goes on. Anything that is not an approved partner continues to the redirect trace and gets a case with timestamped screenshots.
Not every unwanted ad on your brand name is the same problem, so BrandPatrol keeps them in separate case types and checks both against the same roster before either one becomes a case.
Advertisers with no relationship to your brand at all. No partner ID resolves in the redirect chain, no match on your roster, running paid search or shopping ads on your name. The landing page often sells a competing product or a knockoff, or simply captures traffic that should have reached your own site for free.
Affiliates already inside your own program, bidding on your branded terms anyway. The redirect chain resolves to a tracking parameter carrying a partner ID and network. Proof the click ran through your program, which is what makes this a commission problem rather than an outside trademark one.
Both hijacker and brand-bidder detections pass through the same check before a case is ever raised: does the resolved partner ID match someone on your approved list, doing what they're approved to do? If it does, nothing is filed. You only ever see the exceptions.
Getting started takes four inputs from you. Getting access to your systems isn't one of them.
Monitoring reads what any shopper searching your brand would see, plus the ad-transparency record every advertiser is already required to publish. Full detail on data handling lives in our privacy policy.
Every case carries the same fields, whether it's an ad hijacker or a brand bidder. Here's what each one proves.
No monitoring method sees everything. These are the honest constraints that follow from how it actually works.
Detection depends on an ad actually being visible when we look, everything below follows from that.
Questions about a specific edge case? Check the FAQ, or ask when you get a quote.
The questions legal, compliance and affiliate teams ask before they trust a case file. More on coverage and plans is in the full FAQ and on the features page.
BrandPatrol checks the public paid-search results for each agreed keyword, from each agreed location and device, and captures any ad on a branded term with timestamped screenshots. It then follows the click hop by hop, extracts the tracking parameters, and resolves the affiliate ID and network or the advertiser behind the ad.
It takes a timestamped screenshot of the search-results page showing the ad, follows the ad through to wherever it lands, and screenshots that page too, along with the display URL exactly as it was shown. Every redirect hop in between is recorded in order, as covered in how to read a redirect chain.
When the tracking parameters resolve to an affiliate ID and network, that identifies the partner. Where the advertiser is not one of your affiliates, BrandPatrol cross-references the public ad-transparency record that search engines already require, which names who placed the ad. It never relies on the ad's display URL alone.
BrandPatrol only reads public information: search results any shopper would see, plus the public ad-transparency record. It uses no login and no special access, and it observes an ad the way a shopper would, then stops. This is not legal advice, but the method is documented here so your legal or compliance team can evaluate it.
No monitoring method does. An ad has to be serving at scan time to be observed, and rotation, budget pacing and geo-targeting mean a scan samples what is live rather than recording every impression. Higher scan frequency and broader location coverage raise the odds of catching a given ad, but they do not reach 100%.
Before any case is filed, every detection is matched against the list of authorized partners you provide, along with what each one is permitted to do. If it matches an authorized partner doing something they are approved to do, no case is filed. You only see the exceptions.
A case opens with a status your team can act on: new, in progress, solved or muted. BrandPatrol builds the evidence, but enforcement, such as a suspended account, a pulled ad or a commission clawback, is decided by whoever receives the case, not by BrandPatrol.
Get a quote scoped to your keywords, regions, and roster. The same inputs this page just walked through.
Get a quote